Re:Tech
Signed Up for the Free Monitoring? What the Next Eight Weeks Actually Ask of You
Dated5 min read
A breach notification is the start of a small, unglamorous routine, and the difference between a good job and a barely adequate one shows up in week three, not on day one.
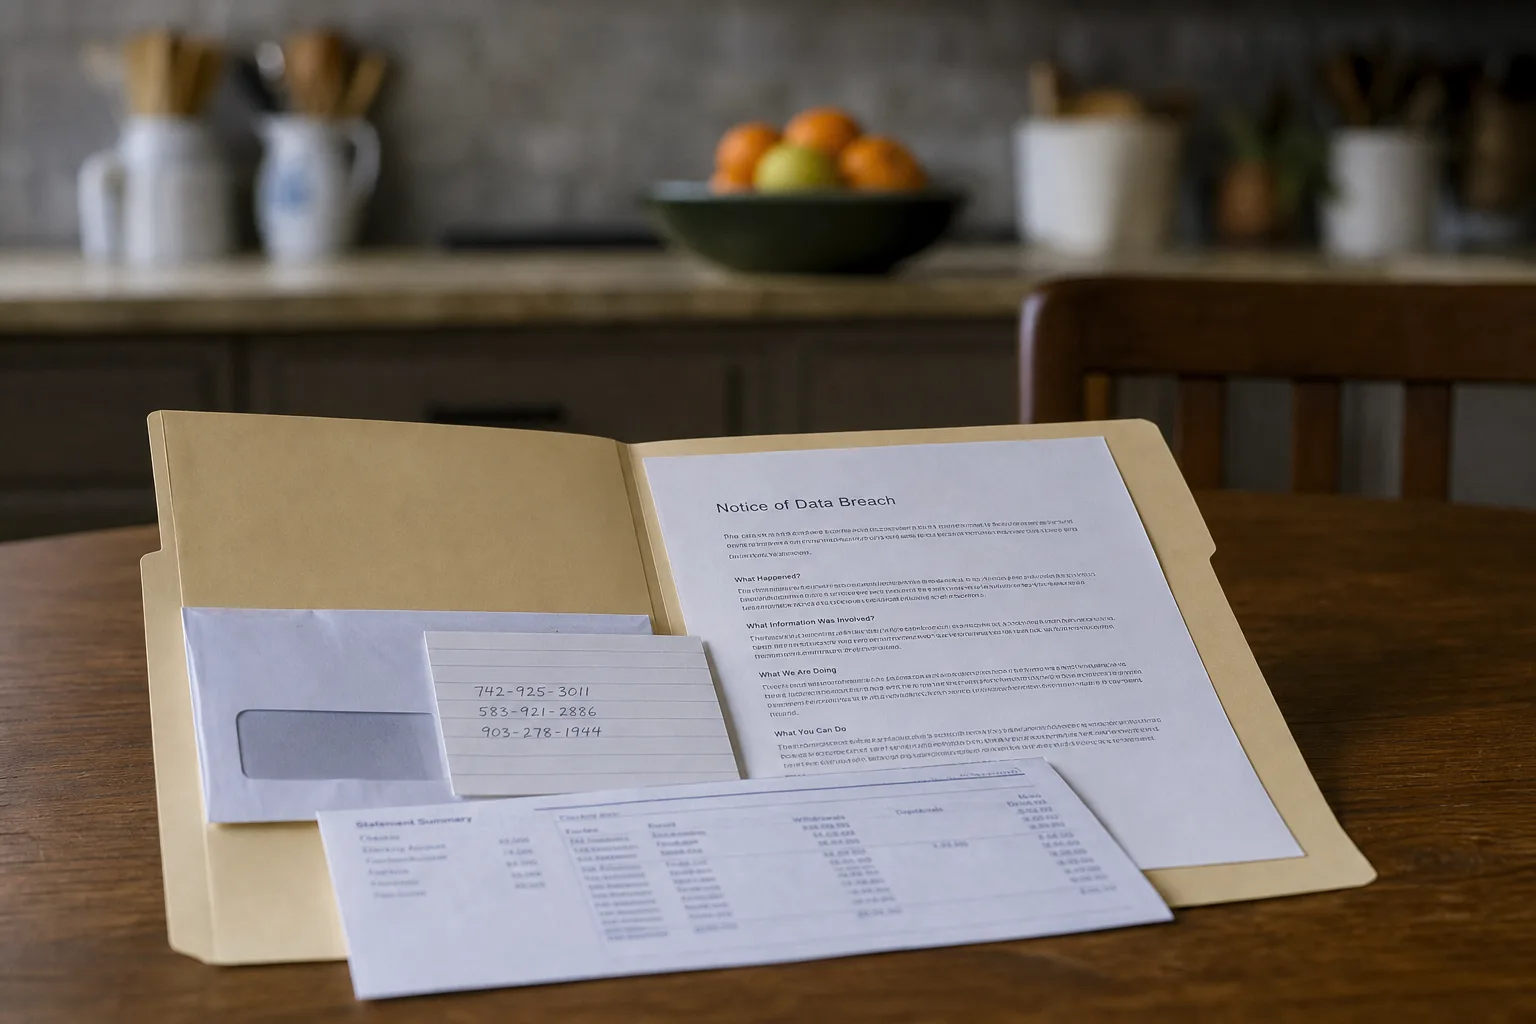
The envelope usually arrives looking like a statement, printed on the same thin stock as an insurance renewal, and the first page is written by a lawyer while the second page is written by a vendor. Most people read both, feel a spike of alarm, click the enrollment link, and then do nothing else for a year. That is the barely adequate version of the job, and it is barely adequate in a specific way: everything it accomplishes happens in one sitting, and nothing it accomplishes survives contact with the following two months.
What a thorough notice tells you, and what a thin one leaves out
Start by reading the letter as a description of scope rather than an apology. A thorough notice names the date range of the intrusion, the date it was discovered, and the specific data elements involved, which is the difference between a name and email address and a Social Security number attached to a date of birth. It says whether files were viewed or copied. A thin notice uses the phrase may have been accessed for everything, gives no date range, and spends its space on the company's commitment to security. The second kind is not necessarily hiding a worse breach, but it leaves you unable to size your own response, so you have to size it upward.
The data elements decide the work. An exposed email address and hashed password means a password change and nothing more, assuming that password lives nowhere else. An account number with a verification code means calling the issuer. A Social Security number, driver's license number, or medical identifier is a different category entirely, because those cannot be rotated the way a password can, and the exposure stays live for years. Keep the letter. Do not file it loose in a drawer where it becomes indistinguishable from a warranty pamphlet three months on.
The first week: the handful of actions you cannot easily undo later
Freezing your credit at each of the three bureaus is free, reversible, and the one step that meaningfully blocks new accounts being opened in your name. Each freeze produces a PIN or an online account, and that credential is now load-bearing. Write it somewhere physical, an index card in a fireproof box or a page in the same folder as the letter, because the failure mode people actually hit is not the freeze, it is being unable to lift the freeze on the Saturday they are sitting in a dealership finance office. A freeze you cannot thaw promptly becomes an obstacle to your own mortgage refinance.
The other first-week actions are quieter. Change the password on the breached account and on anything that shared it, which in most households is two or three services nobody remembers signing up for. Turn on two-factor authentication where it is offered, preferring an authenticator app over text messages. Then set a calendar reminder for the end of the free monitoring term, because those terms expire and the expiration is the moment the vendor's interests and yours diverge.
Weeks two through eight, which is where the real difference shows
Monitoring services generate alerts, and the alerts are mostly noise: an address variant, a soft inquiry, a new authorized user on a card you already knew about. The temptation after four harmless alerts is to stop opening them, and that is precisely the habit the fifth one punishes. The workable routine is narrower than the vendor's defaults. Turn off alerts for things you cannot act on, keep the ones that fire on new accounts, new inquiries, and new addresses, and give the review a fixed slot, ten minutes with coffee on a Sunday, so it does not depend on motivation.
The week-to-week reality is that nothing happens, and then nothing happens again, and the discipline is in keeping a low-effort process alive through the boredom. Check the actual statements rather than a dashboard summary, because a small unfamiliar charge of a few dollars is a test transaction and it often precedes a larger one. Watch your postal mail for account statements from institutions you have no relationship with, which is the oldest and still most reliable signal that something was opened in your name. Paper gets to you whether or not you logged in.
How to read the company's response, and the instant yes problem
Companies offer remediation the way contractors offer availability, and the fastest, most confident answer is not always the strongest one. A good response includes identity restoration, not just monitoring, meaning a named case manager who will file disputes, place calls, and follow the paperwork on your behalf if something is opened fraudulently. A barely adequate response is a twelve-month monitoring enrollment with a code that expires in ninety days and a phone line staffed by people reading a script written in the first week. Ask what happens if you find fraud in month fourteen. The quality of that answer tells you which kind of response you have.
Look for whether the letter tells you something the company had no obligation to share, such as the specific system involved or the fact that a particular field was encrypted and a neighboring one was not. That level of detail costs a company something to disclose and it usually correlates with an internal investigation that actually finished. The Federal Trade Commission is the agency responsible for identity theft reporting and recovery guidance in the United States, and a company pointing you there plainly, rather than only to its own vendor portal, is behaving like an outfit that expects you to verify things.
The folder, and what belongs in it
One manila folder handles nearly all of this. In it: the original letter with the envelope, your freeze PINs, the date you enrolled and the date coverage ends, a printed copy of any dispute you file, and a single sheet where you note calls with the date, the name, and the reference number. If you ever need to prove to a lender, an insurer, or a police department that a charge was not yours, that sheet is the evidence, and reconstructing it from memory nine months later is the part nobody manages.
Most breach letters lead nowhere and the folder stays thin. That is a good outcome, cheaply bought, and the households that handle this well are not the ones who reacted hardest in the first hour. They are the ones who did four irreversible things properly, kept a ten-minute weekly habit for two months, and knew where the PIN was when they needed it.